Expiring download links: temporary access
A time-limited link carries access authority. Expiry, forwarding and saved copies create different boundaries.
The link as a key
Possession of a complete signed download URL may be sufficient for access. Its signature confirms technical conditions rather than the identity of the person accessing it. Such links do not belong in public tickets. Screen recordings can also unintentionally pass on the embedded authority.
Example: a report
An example system creates a short-lived report link after sign-in. A new request fails after expiry. The previously downloaded PDF remains on the receiving device. Expiry limits server access; it does not make previously distributed copies disappear.
The process at a glance
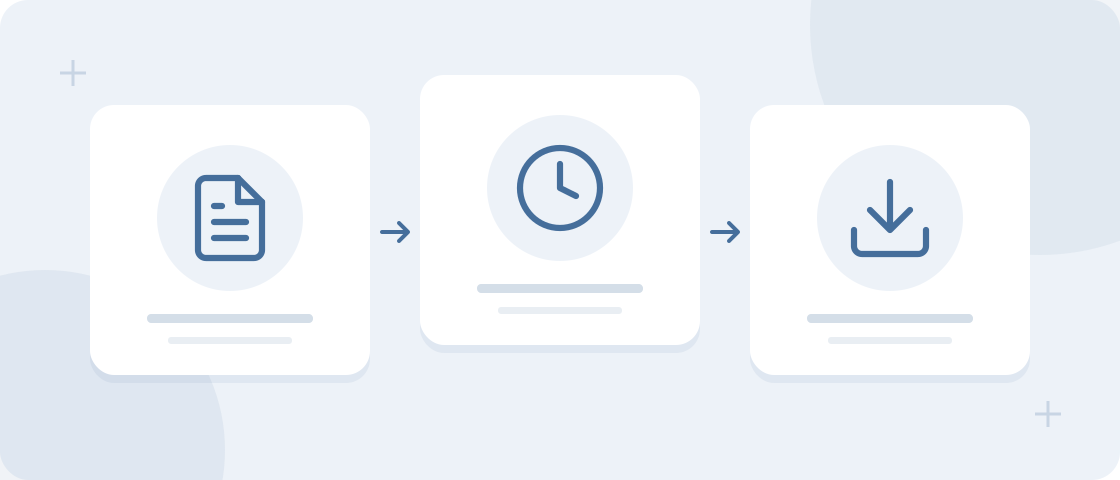
- PermissionOne report
- DownloadValid time window
- ExpiryNew requests blocked
Considering revocation separately
Testing covers fresh, expired and forwarded links. Behaviour after the original permission is removed matters too. Immediate revocation may require separate blocking logic. Product documentation should explain this behaviour and identify responsibility for links accidentally made public.